Katja Hoffmann · 18 October 2026
Exploring Encryption Protocols and Data Security Measures in Restricted Online Membership Platforms
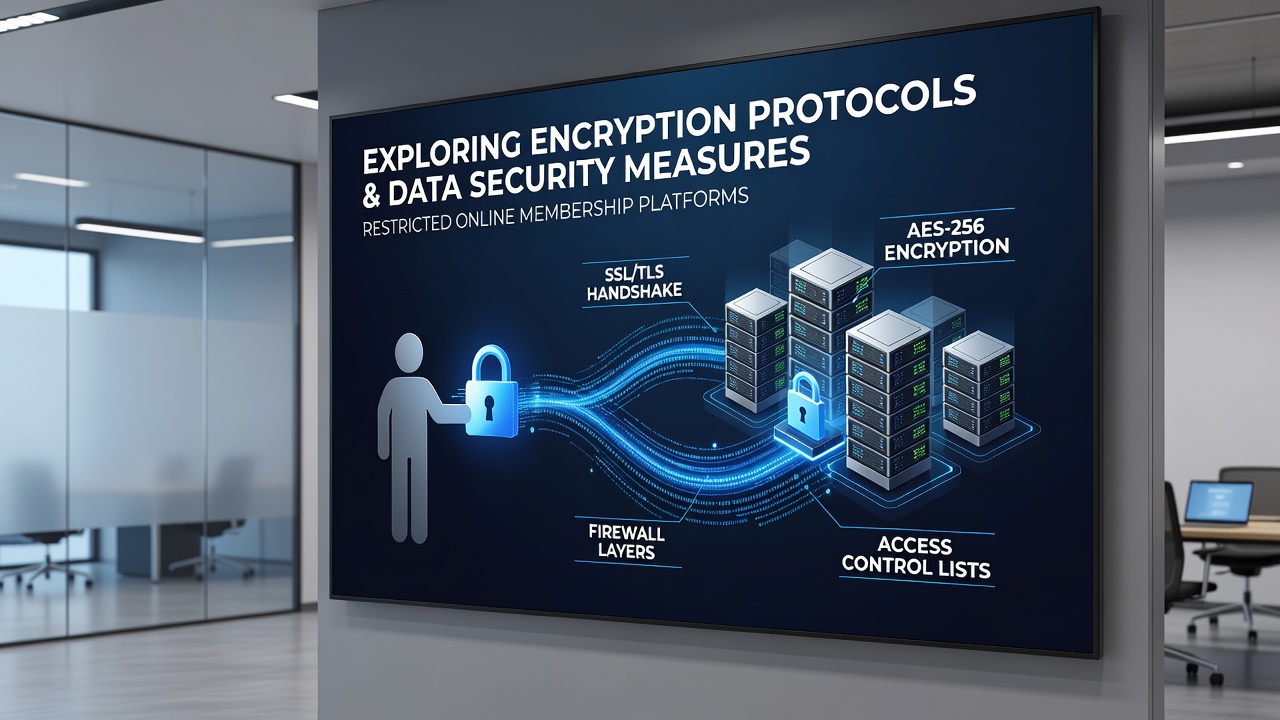
Restricted online membership platforms operate with layers of access controls that limit entry to verified participants, and encryption protocols form the backbone of protecting communications and stored information within these environments. These systems rely on established standards for securing data both during transmission and while at rest, with protocols such as TLS 1.3 handling secure connections and AES-256 providing symmetric encryption for stored records. Observers note that platforms often integrate end-to-end encryption to ensure that even service providers cannot access content without user-held keys, a practice that aligns with recommendations from bodies like the National Institute of Standards and Technology.
Access management in these platforms combines encryption with authentication mechanisms including multi-factor methods and certificate-based verification, while regular key rotation schedules reduce risks from potential compromises. Researchers have documented how zero-knowledge architectures allow platforms to verify membership status without retaining identifiable details, thereby limiting exposure during audits or breaches. Data segmentation further isolates user information into encrypted compartments, so a single point of failure does not compromise entire databases.
Core Encryption Protocols in Use
Transport Layer Security version 1.3 serves as the current standard for encrypting data in transit across restricted networks, offering forward secrecy that prevents decryption of past sessions even if long-term keys are exposed later. Platforms apply this protocol to all API calls and member interactions, and many supplement it with additional measures such as certificate pinning to block man-in-the-middle attempts. At rest, AES-256 encryption protects files and database entries, with keys managed through hardware security modules that store credentials separately from the main infrastructure.
Post-quantum cryptography preparations have accelerated in advance of anticipated regulatory shifts, and by October 2026 several platforms are expected to begin testing lattice-based algorithms alongside existing systems to maintain security against future quantum threats. Those who manage these environments often reference guidelines from the European Union Agency for Cybersecurity when selecting hybrid approaches that combine classical and emerging methods.
Additional Security Layers and Implementation Patterns
Behavioral analytics complement encryption by monitoring login patterns and flagging anomalies that could indicate unauthorized attempts, triggering automatic session terminations or additional verification prompts. Audit logs remain encrypted themselves and require multiple approvals for access, which creates accountability without exposing sensitive records. One documented case involved a platform that detected an internal key-handling error through routine integrity checks and resolved it before any data left the system boundaries.
Compliance frameworks influence protocol choices as well, since platforms serving members across regions must satisfy varying requirements on data residency and breach notification timelines. Industry reports indicate that organizations adopting automated key management systems experience fewer operational disruptions during updates, because these tools handle rotation without manual intervention. Restricted environments also employ containerization to run encrypted processes in isolated instances, reducing the attack surface available to external actors.
Challenges and Ongoing Adaptations
Key distribution presents ongoing difficulties in invitation-only settings where new members must receive credentials securely without relying on public channels. Platforms address this through out-of-band methods such as encrypted messaging apps or physical tokens that deliver initial access codes. Performance considerations arise when heavy encryption loads affect response times, yet optimized implementations maintain usability while preserving security standards.
Training programs for administrators focus on recognizing social engineering tactics that target encryption key holders, and simulation exercises help teams practice responses to simulated incidents. Evidence from sector analyses shows that platforms conducting quarterly penetration tests identify configuration weaknesses earlier than those relying on annual reviews alone. Integration with hardware-based authenticators further strengthens defenses against credential theft attempts.
Conclusion
Encryption protocols and layered security measures continue to evolve in response to emerging threats and regulatory timelines, with restricted membership platforms serving as testing grounds for advanced implementations. Standards from organizations including the National Institute of Standards and Technology and the European Union Agency for Cybersecurity provide reference points that guide these developments. As October 2026 approaches, preparations for post-quantum transitions highlight the ongoing need for adaptable frameworks that protect member data without compromising platform functionality.